Silent Killers: Unmasking a Large-Scale Legacy Driver Exploitation Campaign#
hack.lu 2025 digest Program Adjacent pick 21–24 October 2025
Jiří Vinopal (Check Point Research)
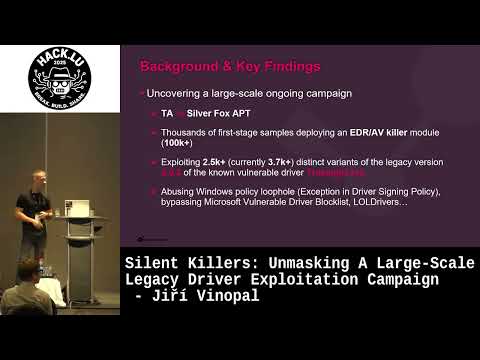
- Why: A measured, large-scale proof that hash-based and allowlist-based driver defenses (including Microsoft's Vulnerable Driver Blocklist) can be defeated at industrial scale — important context for any endpoint defense stack.
- What: A 2025 campaign using 2,500+ uniquely modified but still validly-signed variants of Truesight.sys v2.0.2 (the RogueKiller anti-rootkit driver) to kill EDR/AV. Version 2.0.2 was chosen specifically because it retains the vulnerability while falling below the Microsoft blocklist's and LOLDrivers' coverage; PE structure was manipulated to change hashes while preserving the signature. ~75% of victims are in China, remainder in other parts of Asia; MSRC updated the blocklist on Dec 17, 2024 in response. (from abstract only)
- How: Phishing-distributed first-stage loaders (disguised as known applications) exploit a Windows driver-signing policy exception to load the legacy driver, deploy an EDR/AV killer module, and prep the machine for final payloads such as Gh0st RAT variants; C2 hosted in a public cloud's China region.
- Where applicable: Windows EDR/AV deployments relying on the driver blocklist; loading the driver requires admin-level execution on the victim (phishing initial access). Vendor-neutral lesson, Windows-specific mechanics.